
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS…
Key facts
- Attack vector
- Network
- Privileges required
- High
- User interaction
- None
- Attack complexity
- Low
- Impact type
- Information disclosure
- Confidentiality · integrity · availability
- High · High · High
- Fix status
- No fix listed
Attack profile from CVSS 3.0 · NVD. Fix status from CNA. Impact type from CWE-312.
Summary
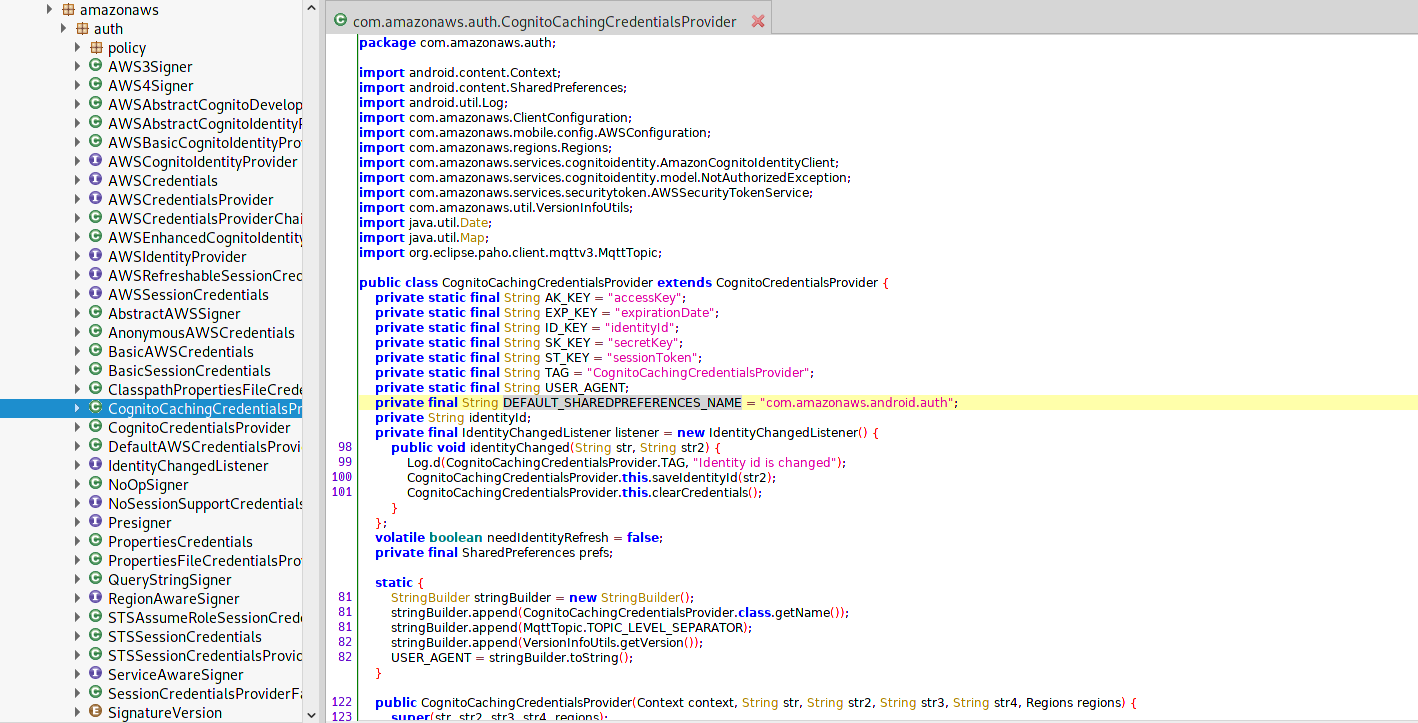
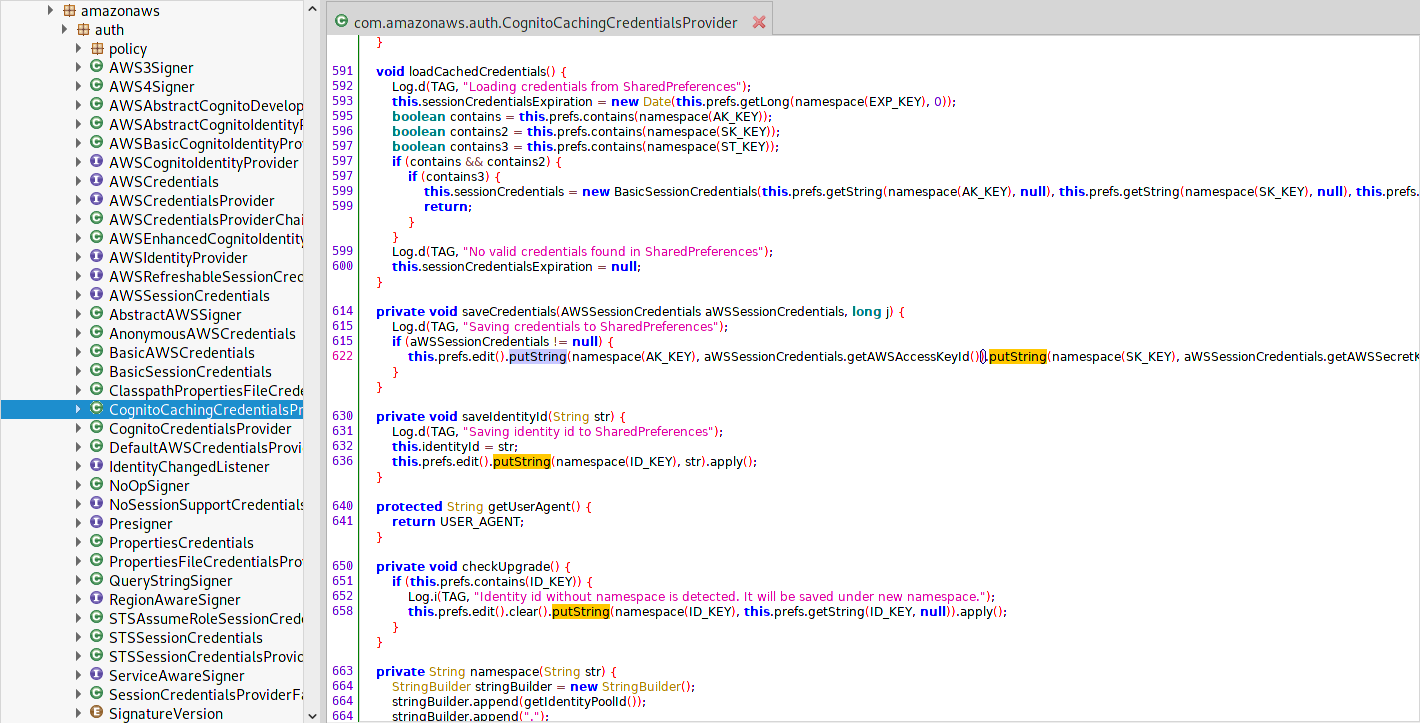
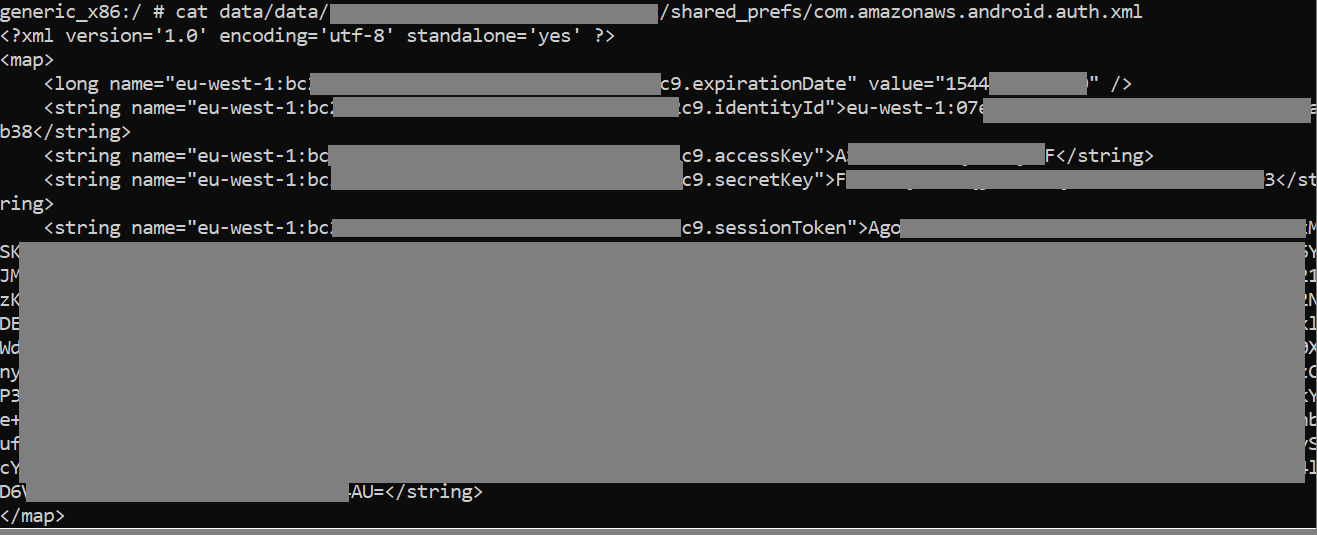
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
Why it matters now
SSVC decision points
Not available: CISA has not published SSVC decision points for this record.
Affected products
| Vendor | Product | Affected versions | Fixed in | Status | Source |
|---|---|---|---|---|---|
| — | — | all versions | — | No fix listed | CNA |
- — Vendor— Affected all versions Fixed in — No fix listed CNA
Remediation
No fixed version listed by the sources yet.
Timeline
- 2026-10-02 Threatist record created from CVE-2018-19981
- 2026-10-03 Alias added: GHSA-4rp2-whvp-25jm
References
Exploit 4
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_02.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_03.png
- https://aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html
More Aws Software Development Kit vulnerabilities
- TI-2022-04321 AWS SDK XML Parser XpathUtils.java XpathUtils server-side request forgery CVSS 3.1CRITICAL 9.8
- TI-2026-15952 Out-of-bounds read in the Base64 decoder in Amazon aws-sdk-cpp on signed-char platforms CVSS 4.0MEDIUM 6.0
- TI-2026-15951 Out-of-bounds write in the Base64 decoder in Amazon aws-sdk-cpp CVSS 4.0MEDIUM 6.0
- TI-2023-28302 Potential URI resolution path traversal in the AWS SDK for PHP CVSS 3.1MEDIUM 6.0
- TI-2022-02384 Exposure of unencrypted plaintext hash in github.com/aws/aws-sdk-go CVSS 3.1MEDIUM 4.3
Sources
- CVE-2018-19981 · CVE Program
- CVE-2018-19981 · NVD
- FIRST EPSS
- GHSA-4rp2-whvp-25jm · GitHub Advisory Database · CC BY 4.0
This product uses the NVD API but is not endorsed or certified by the NVD. Sources and licences