
pyLoad's Session Not Invalidated After Permission Changes
Key facts
- Attack vector
- —
- Privileges required
- —
- User interaction
- —
- Attack complexity
- —
- Impact type
- Security bypass
- Confidentiality · integrity · availability
- —
- Fix status
- No fix listed
No CVSS vector from any source. Fix status from GitHub. Impact type from CWE-613.
Summary
### Summary The `pyload` application does not properly invalidate or modify sessions upon changes made to a user's permissions. ### Details Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions. ### PoC Take a user with all the permissions, as shown below. 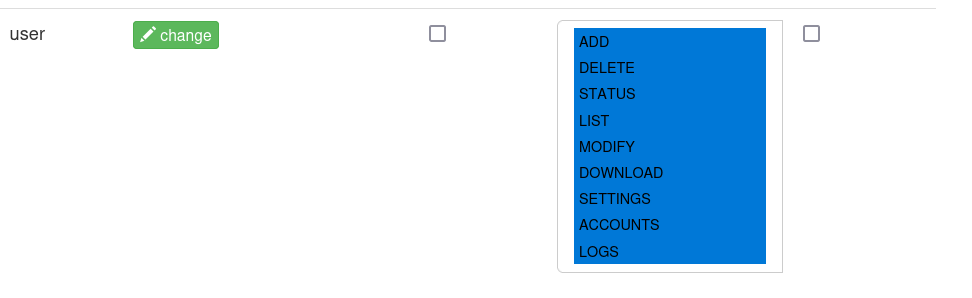 We now log in as this user. 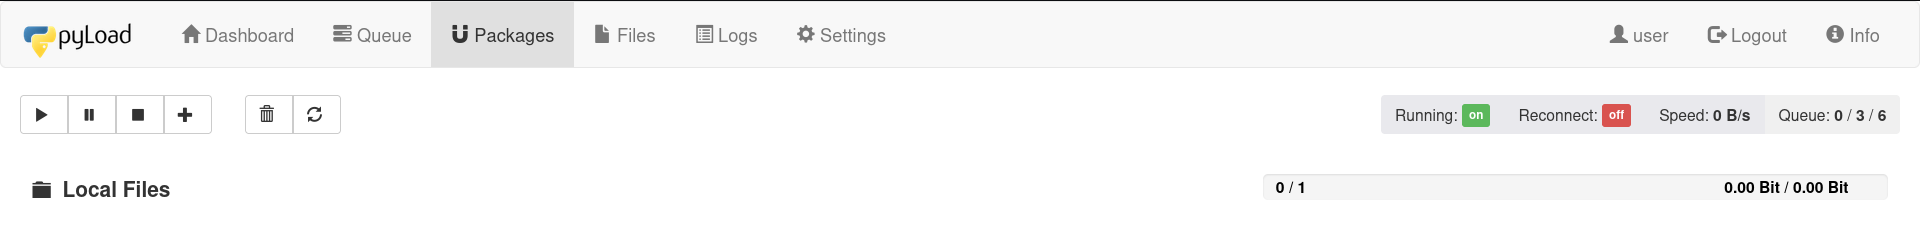 Let us now take away all the permissions. 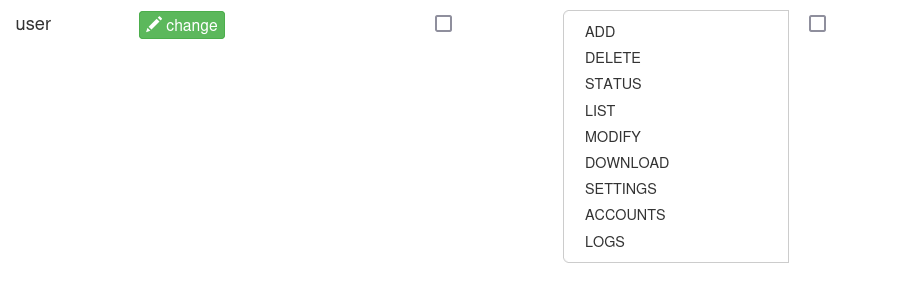 The logged in session can still be used to access everything in the application. 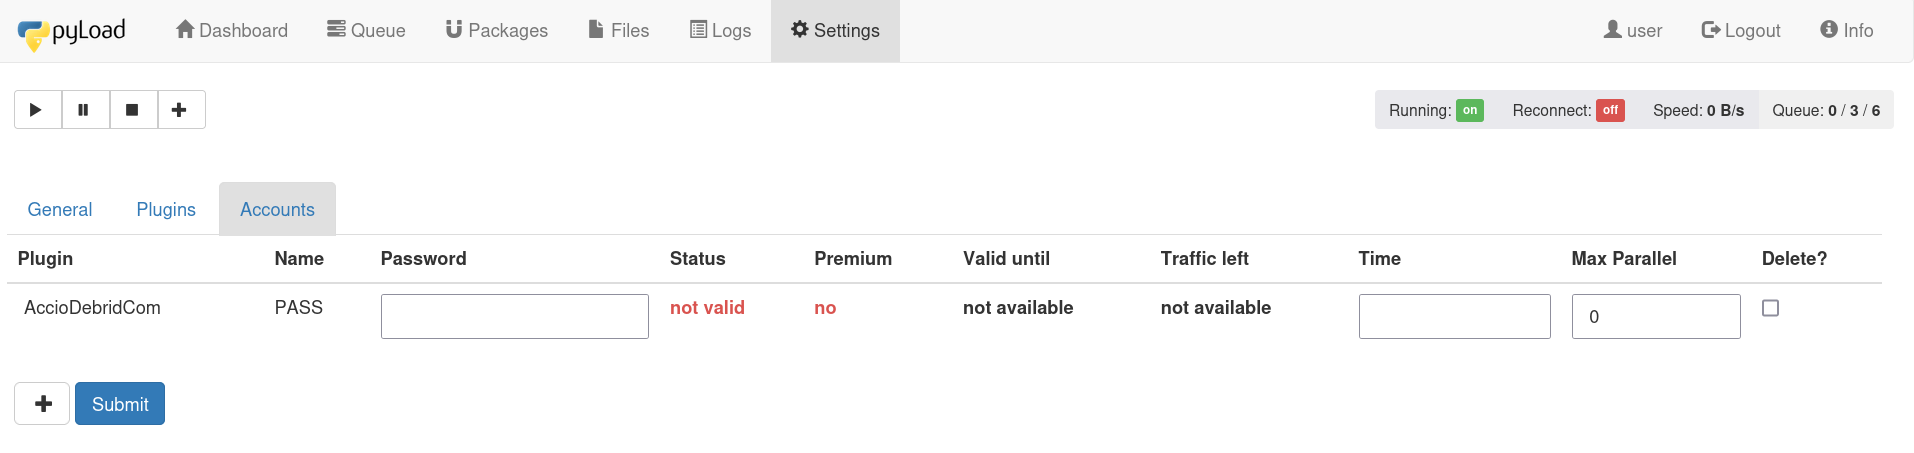 ### Impact Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
Why it matters now
SSVC decision points
Not available: CISA has not published SSVC decision points for this record.
Affected products
| Vendor | Product | Affected versions | Fixed in | Status | Source |
|---|---|---|---|---|---|
| — | pyload-ng (PyPI) | up to 0.5.0b3.dev97 | — | No fix listed | GHSA-fj52-5g4h-gmq8 |
- pyload-ng (PyPI) Vendor— Affected up to 0.5.0b3.dev97 Fixed in — No fix listed GHSA-fj52-5g4h-gmq8
Remediation
No fixed version listed by the sources yet.
Timeline
- 2026-10-03 Threatist record created from GHSA-fj52-5g4h-gmq8
References
Sources
This product uses the NVD API but is not endorsed or certified by the NVD. Sources and licences