
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Key facts
- Attack vector
- Network
- Privileges required
- None
- User interaction
- Required
- Attack complexity
- Low
- Impact type
- Cross-site scripting
- Confidentiality · integrity · availability
- Low · Low · None
- Fix status
- Fixed
Attack profile from CVSS 3.1 · NVD. Fix status from CNA and GitHub. Impact type from CWE-79.
Summary
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 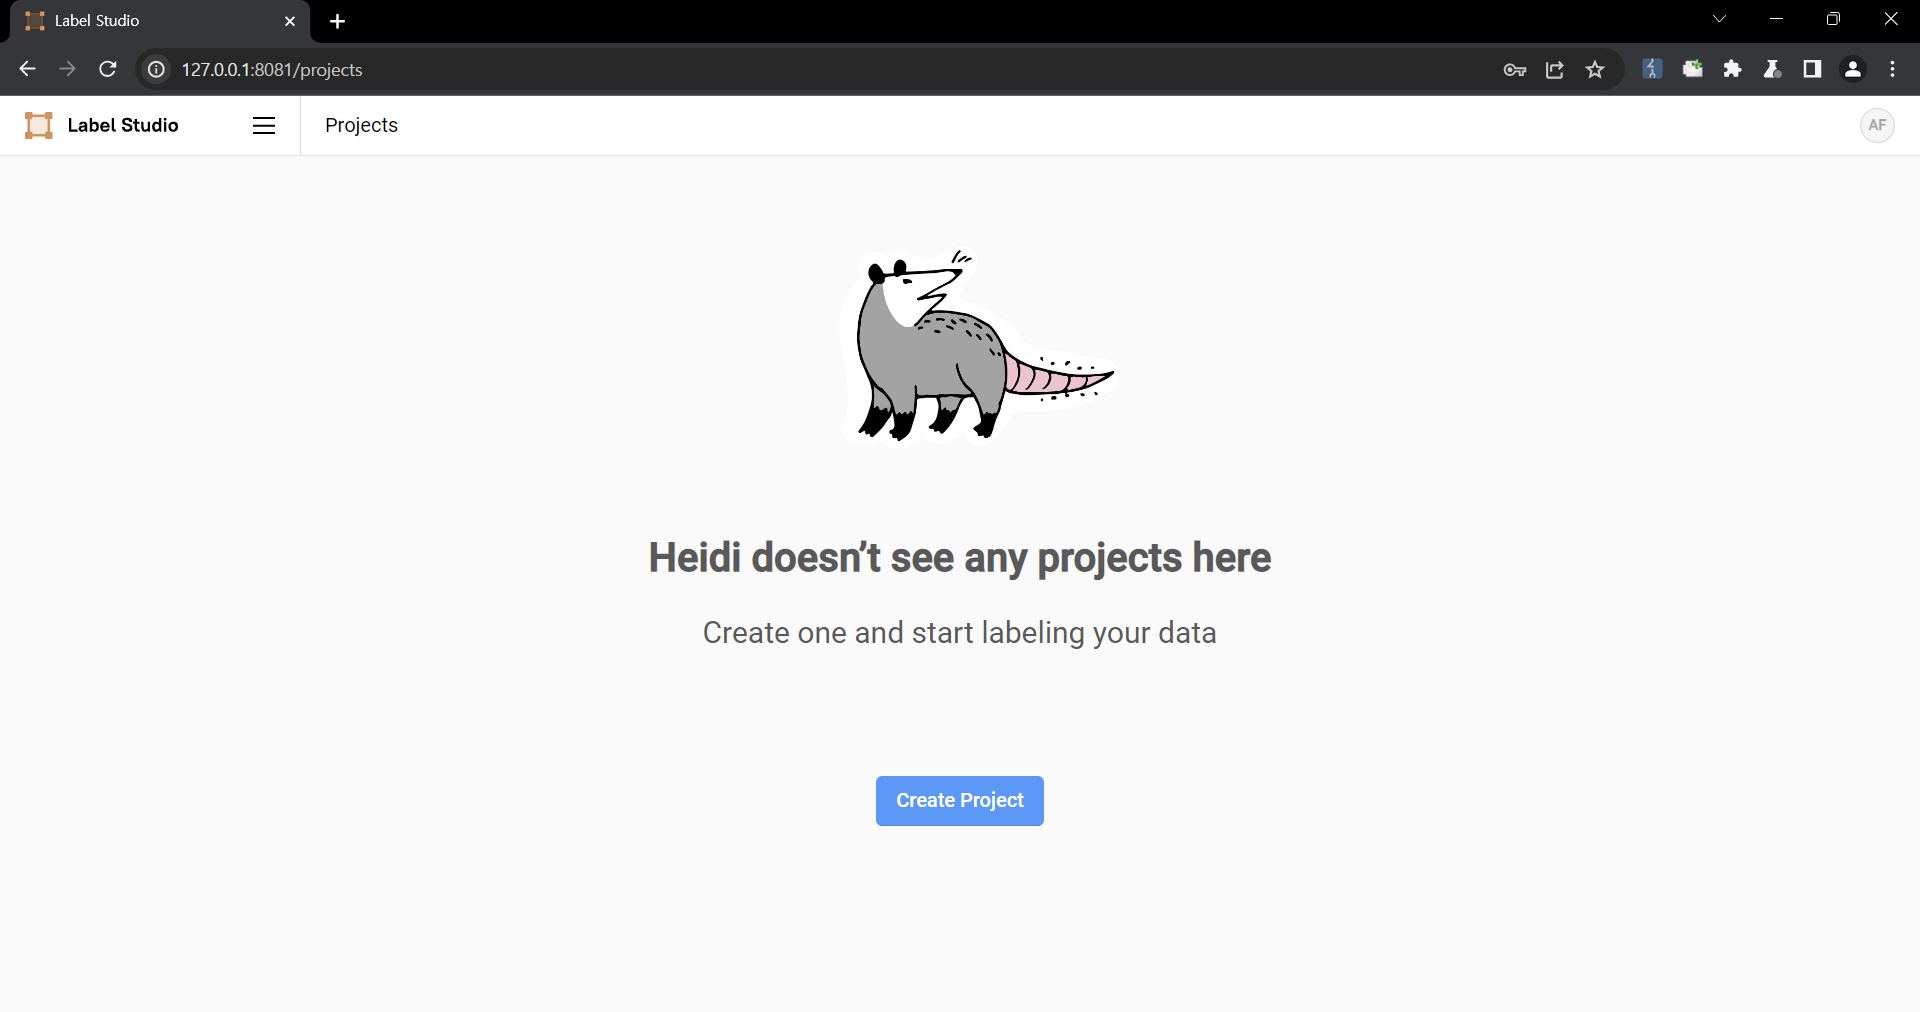 2. Upload a file containing the payload using the "Upload Files" function. 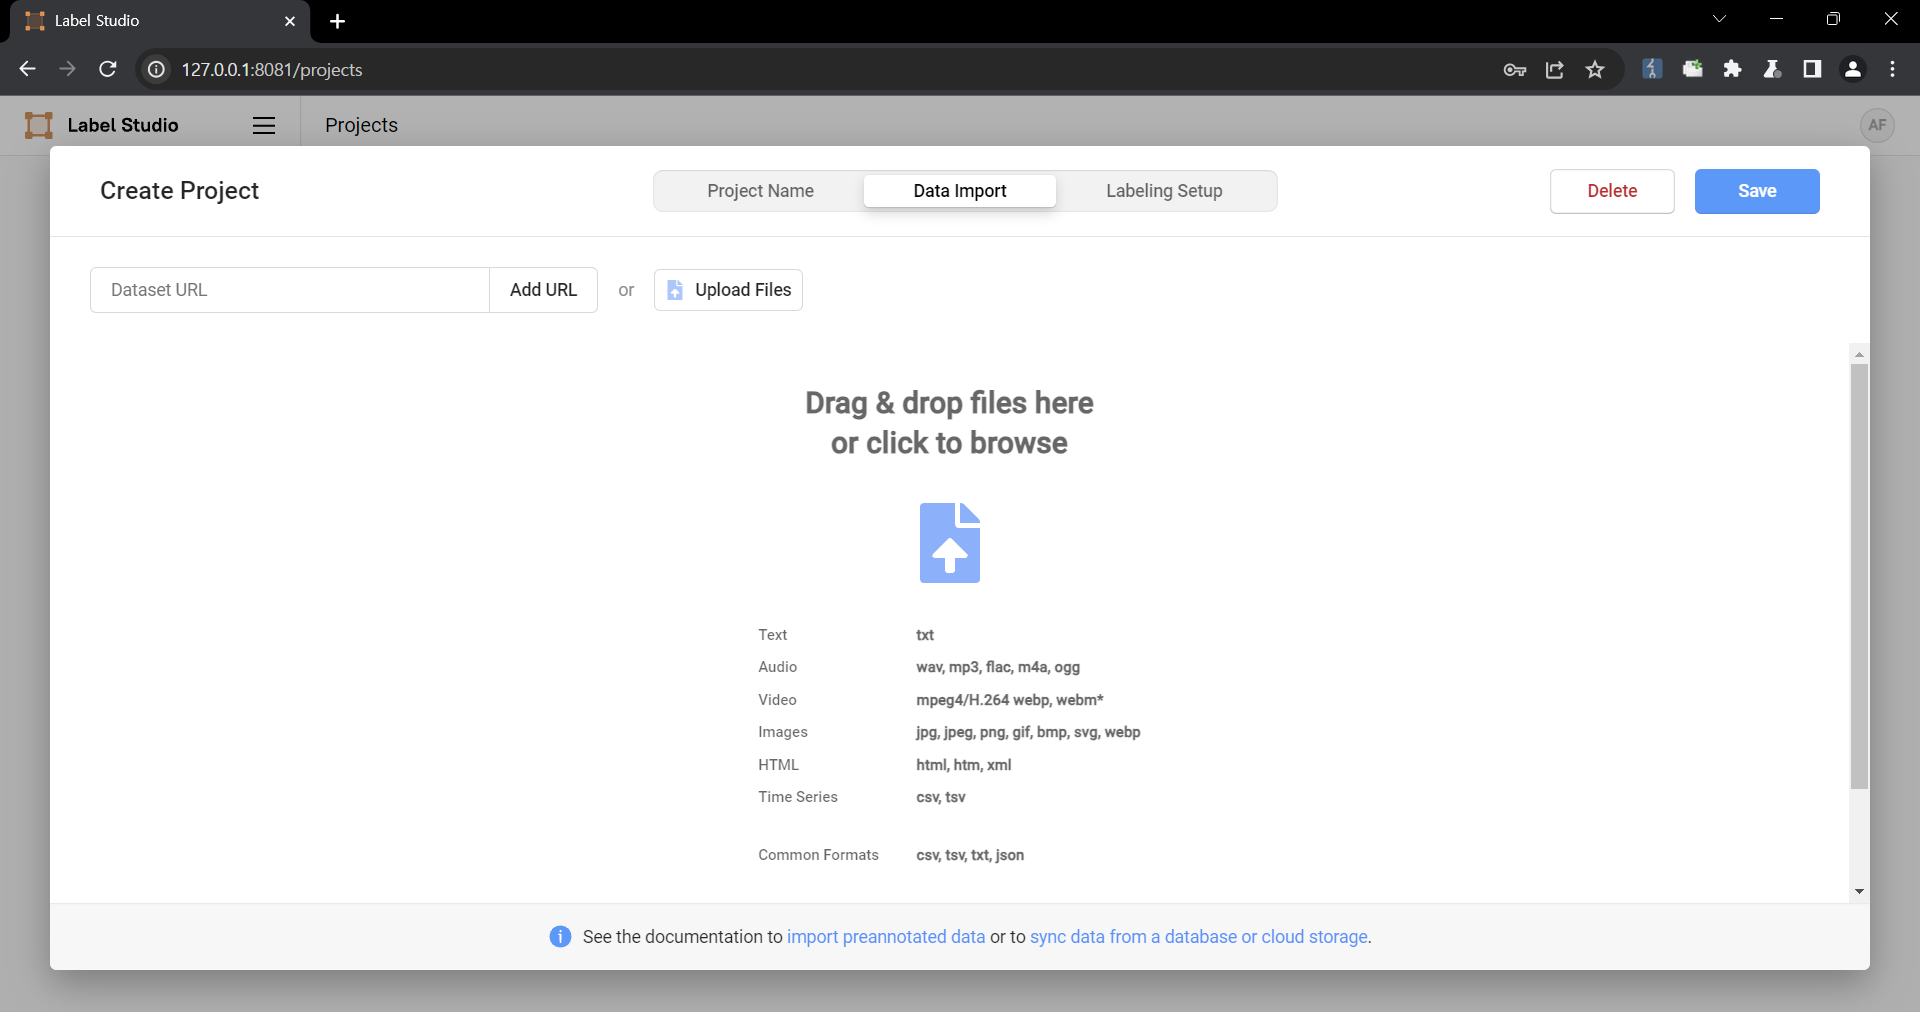 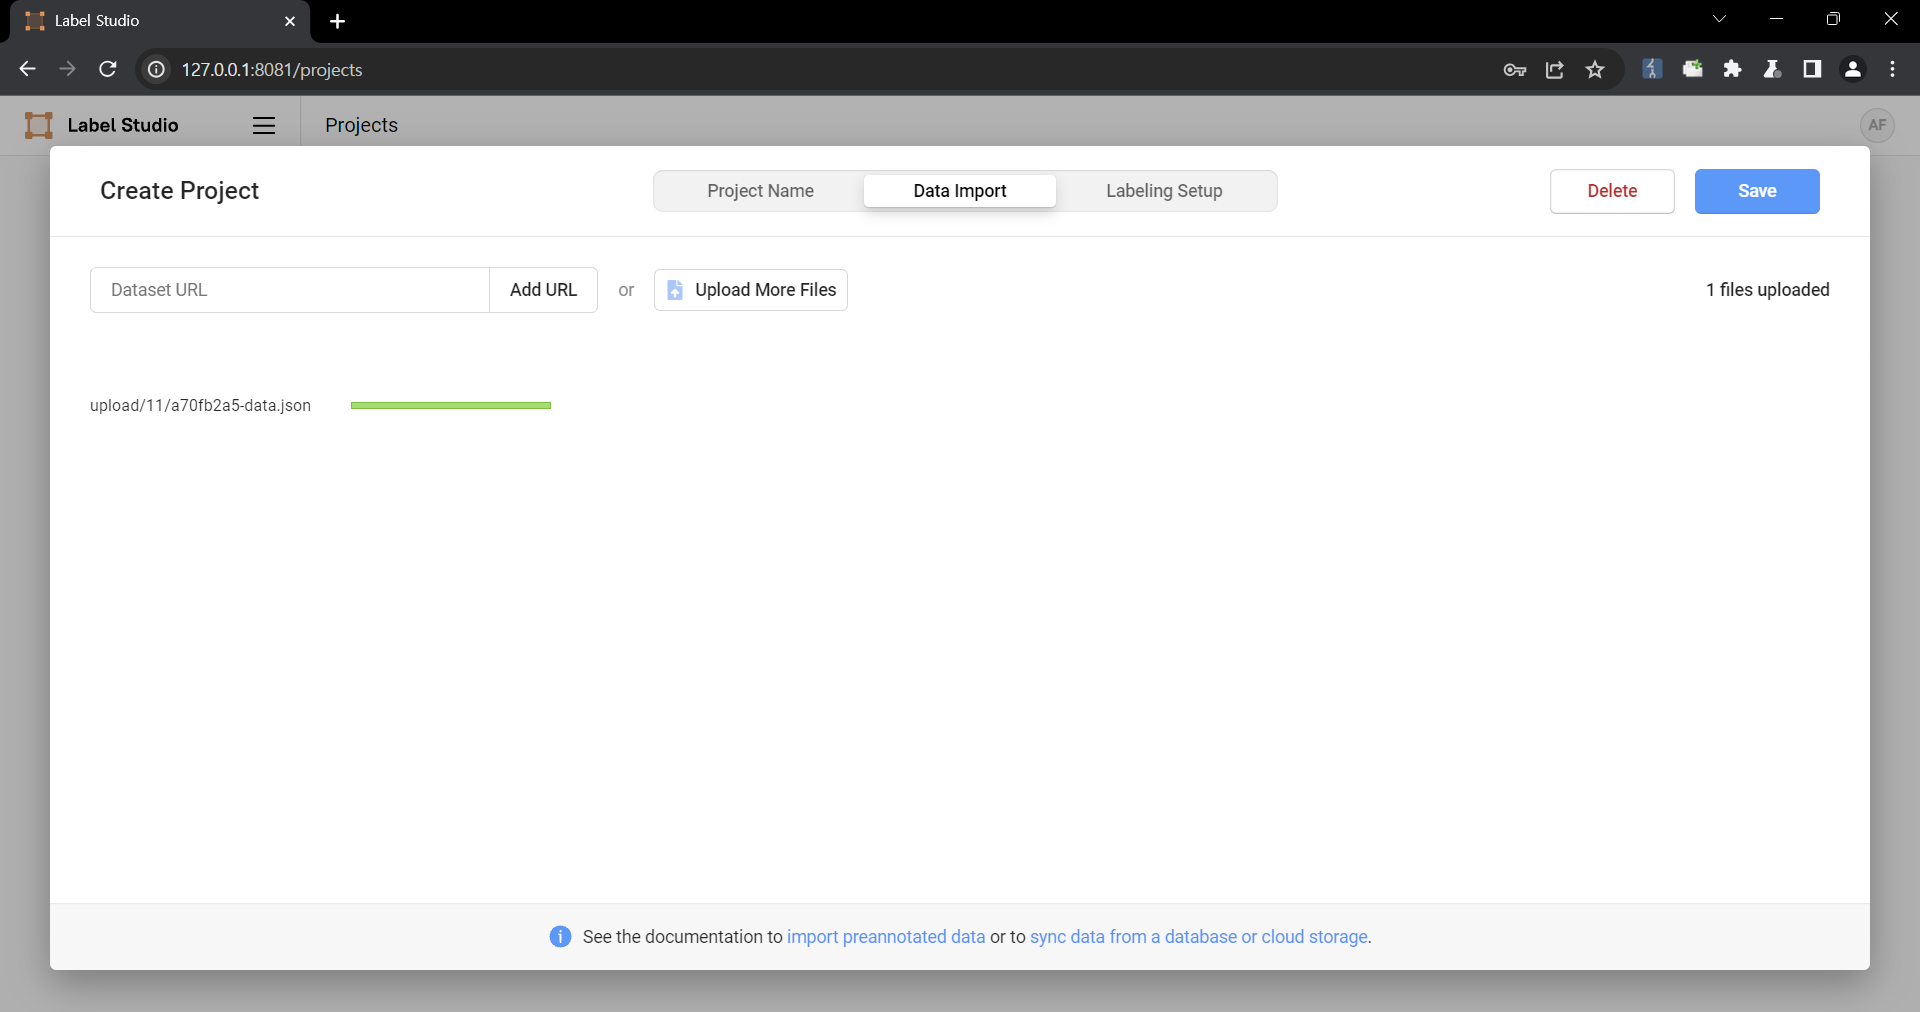 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 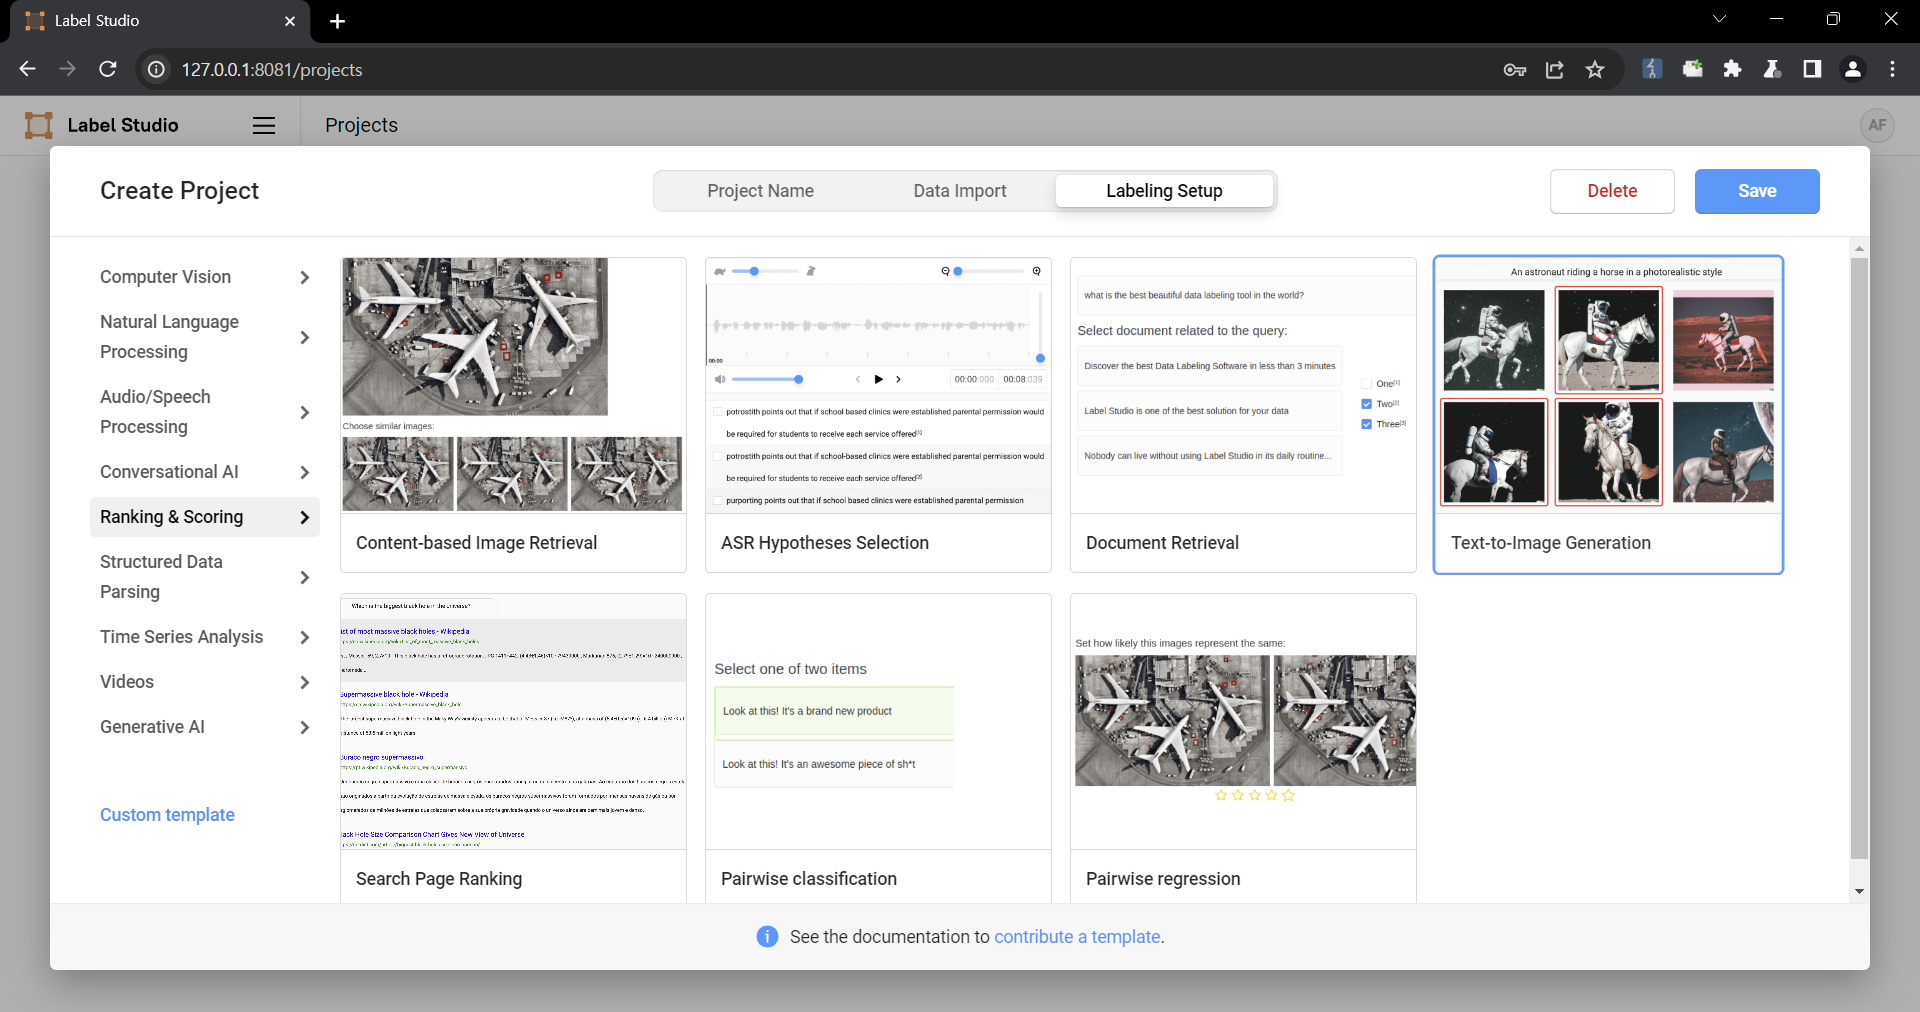 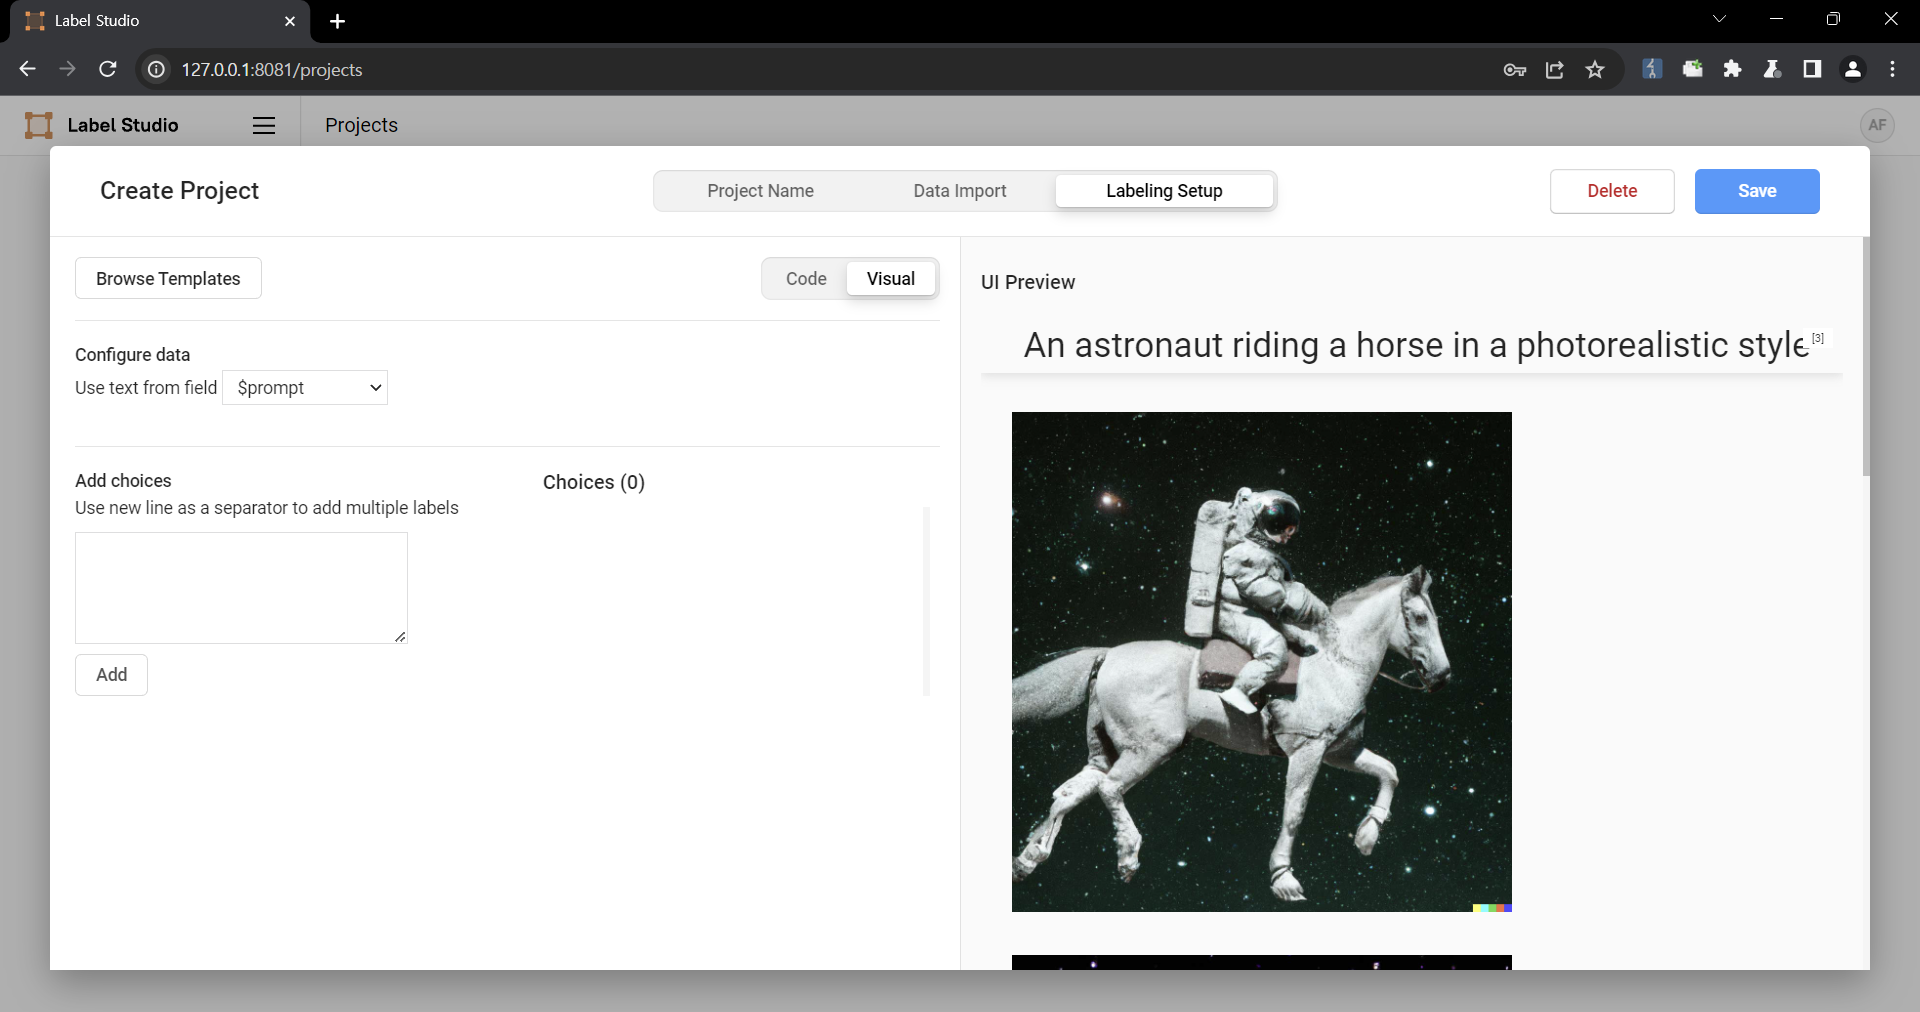 4. Select a task 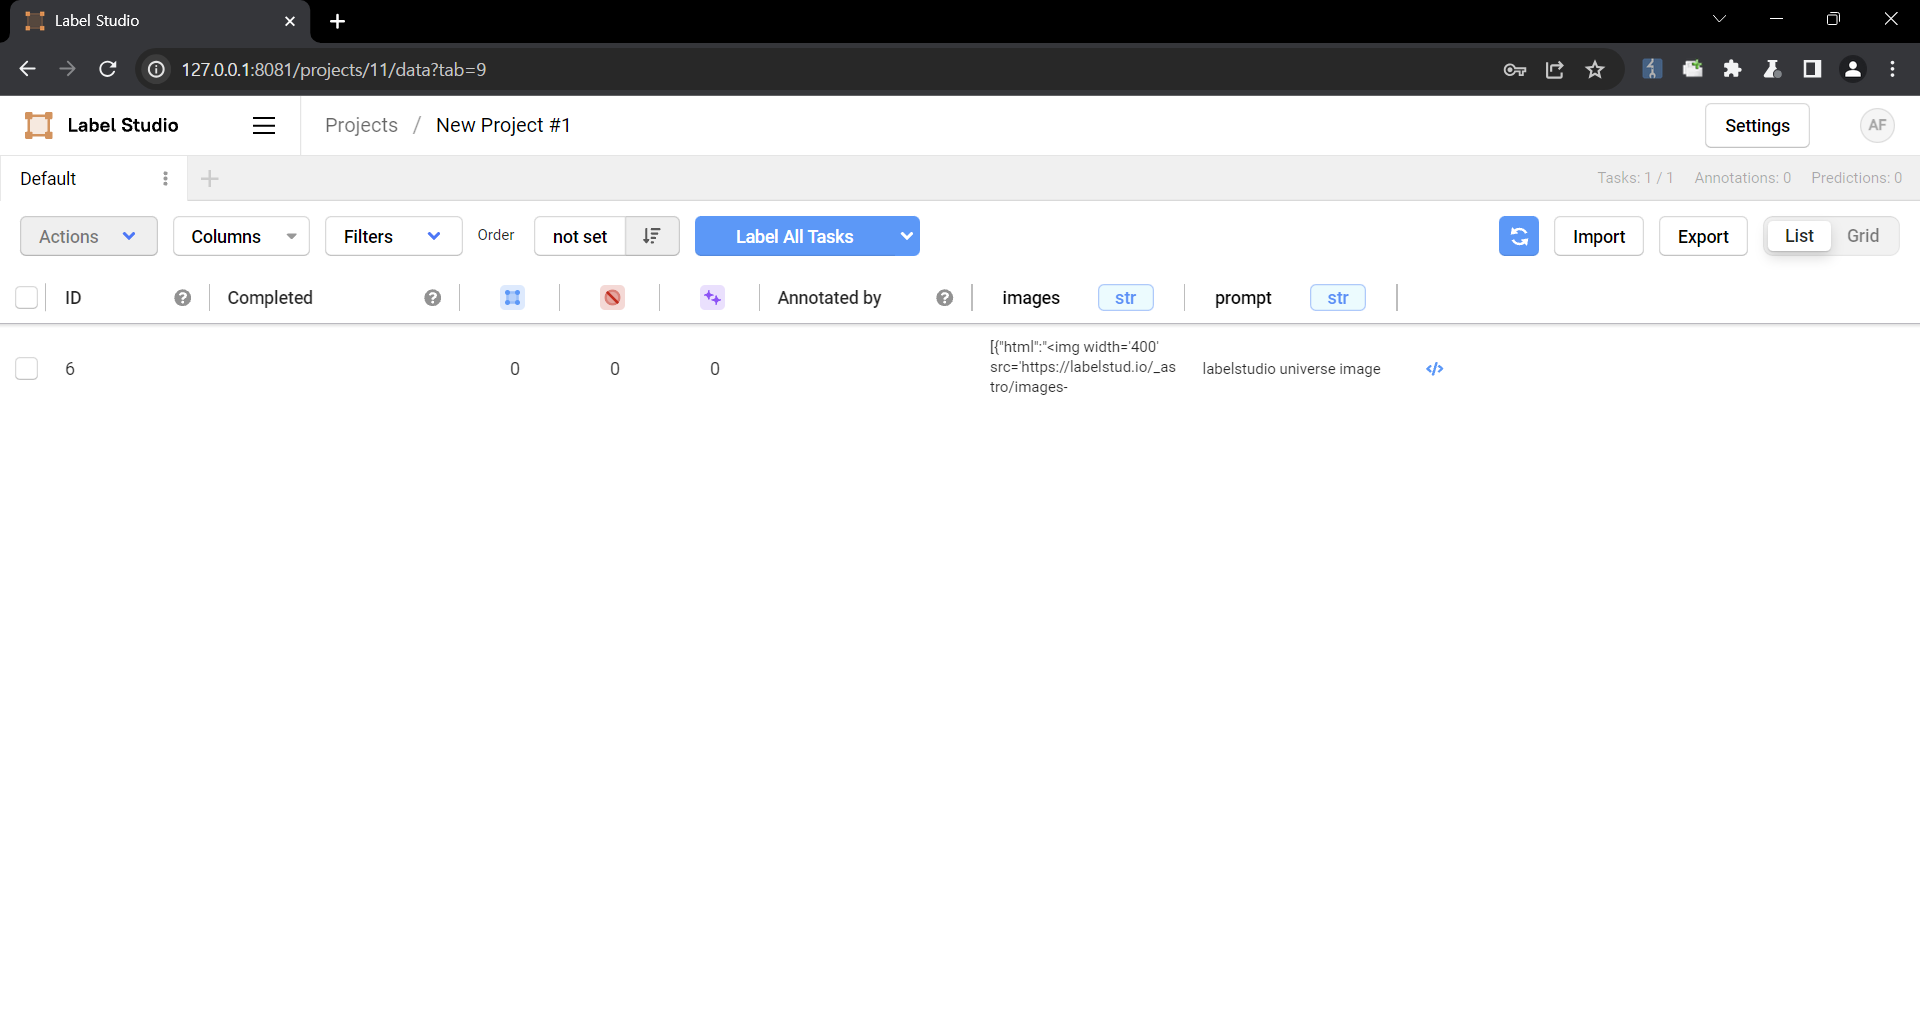 5. Check that the script is running 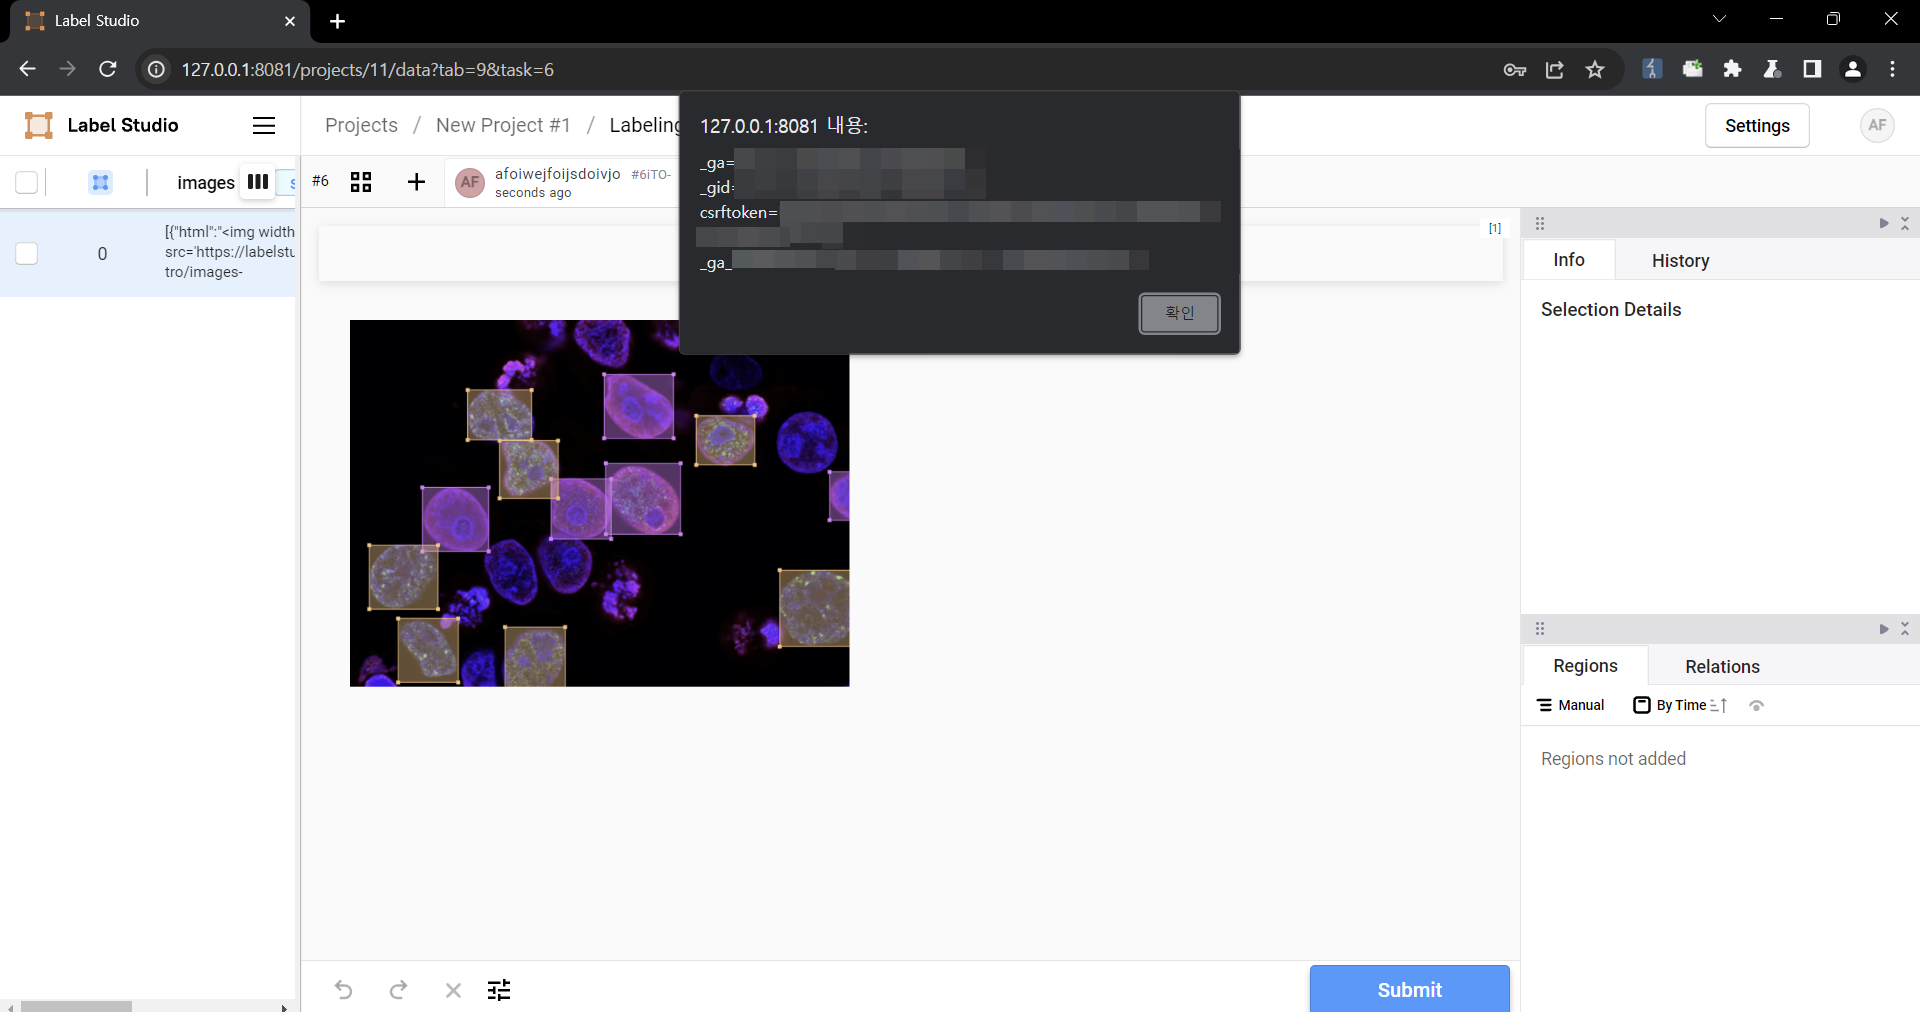 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Why it matters now
SSVC decision points
CISA ADP · SSVC 2.0.3
- Exploitation
- Poc
- Automatable
- No
- Technical impact
- Partial
The decision (Track, Attend, Act) also depends on your mission and well-being impact; see CISA's SSVC guide.
Affected products
| Vendor | Product | Affected versions | Fixed in | Status | Source |
|---|---|---|---|---|---|
| HumanSignal | label-studio | before 1.11.0 | 1.11.0 | Patch available | CNA |
| — | label-studio (PyPI) | before 1.11.0 | 1.11.0 | Patch available | GHSA-6xv9-957j-qfhg |
- label-studio VendorHumanSignal Affected before 1.11.0 Fixed in 1.11.0 Patch available CNA
- label-studio (PyPI) Vendor— Affected before 1.11.0 Fixed in 1.11.0 Patch available GHSA-6xv9-957j-qfhg
CPE configurations NVD · 1
| CPE | Versions | Role | Vendor |
|---|---|---|---|
| cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:* | before 1.11.0 | Vulnerable | HumanSignal |
- cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:* Versions before 1.11.0 Vulnerable ·HumanSignal
Remediation
- Fix · CNA label-studio (HumanSignal) Fixed in 1.11.0
- Fix · GHSA-6xv9-957j-qfhg label-studio (PyPI) Fixed in 1.11.0 Advisory →
Timeline
- 2026-10-02 Threatist record created from CVE-2024-26152
- 2026-10-03 Alias added: GHSA-6xv9-957j-qfhg
References
Patch 2
More HumanSignal Label Studio vulnerabilities
- TI-2023-23482 Label Studio has Hardcoded Django `SECRET_KEY` that can be Abused to Forge Session Tokens CVSS 3.1CRITICAL 9.8
- TI-2025-18951 Label Studio allows Server-Side Request Forgery in the S3 Storage Endpoint CVSS 3.1HIGH 8.6
- TI-2023-25457 Object Relational Mapper Leak Vulnerability in Filtering Task in Label Studio CVSS 3.1HIGH 7.5
- TI-2026-17727 Label Studio vulnerable to full account takeover by chaining Stored XSS + IDOR in User Profile via custom_hotkeys field CVSS 4.0HIGH 8.6
- TI-2025-30248 label-studio vulnerable to Cross-Site Scripting (Reflected) via the label_config parameter. CVSS 4.0HIGH 7.6
- TI-2023-25455 Label Studio XSS Vulnerability on Avatar Upload CVSS 3.1HIGH 7.1
Sources
- CVE-2024-26152 · CVE Program
- CVE-2024-26152 · NVD
- FIRST EPSS
- GHSA-6xv9-957j-qfhg · GitHub Advisory Database · CC BY 4.0
This product uses the NVD API but is not endorsed or certified by the NVD. Sources and licences